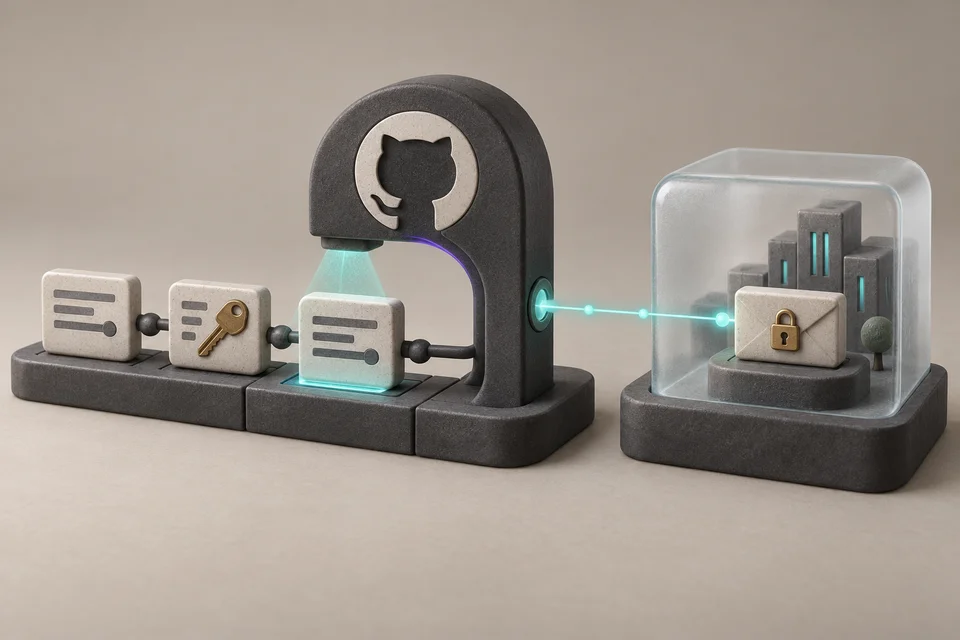
GitHub Enterprise Cloud administrators using data residency can now enable public monitoring in public preview. The feature extends secret scanning beyond internal repositories by monitoring public commits on github.com and alerting enterprises to exposed credentials attributed to them. It requires an active GitHub Advanced Security or GitHub Secret Protection license and carries no additional charge.
Attribution relies exclusively on a commit author’s email matching a verified enterprise domain; enterprise membership rosters are not shared across the isolation boundary. GitHub says alerts are encrypted and delivered to the enterprise dashboard while keeping data within the designated geography. Enterprise admins and enterprise security managers can enable the preview in enterprise security settings.
Choose a sign-in method or comment as a guest below.